Modules · Data protection (GDPR)

Your GDPR obligations, met and evidenced in one place.

Record of processing, data subject requests, breaches, impact assessments, processors: Ecaldima brings the data protection officer’s tools into the application that processes the data. Every step leaves its evidence; the decisions remain theirs.

Request a demonstration

  • Record proposed by the modules
  • 72-hour deadline tracked continuously
  • Dated file, ready for an inspection
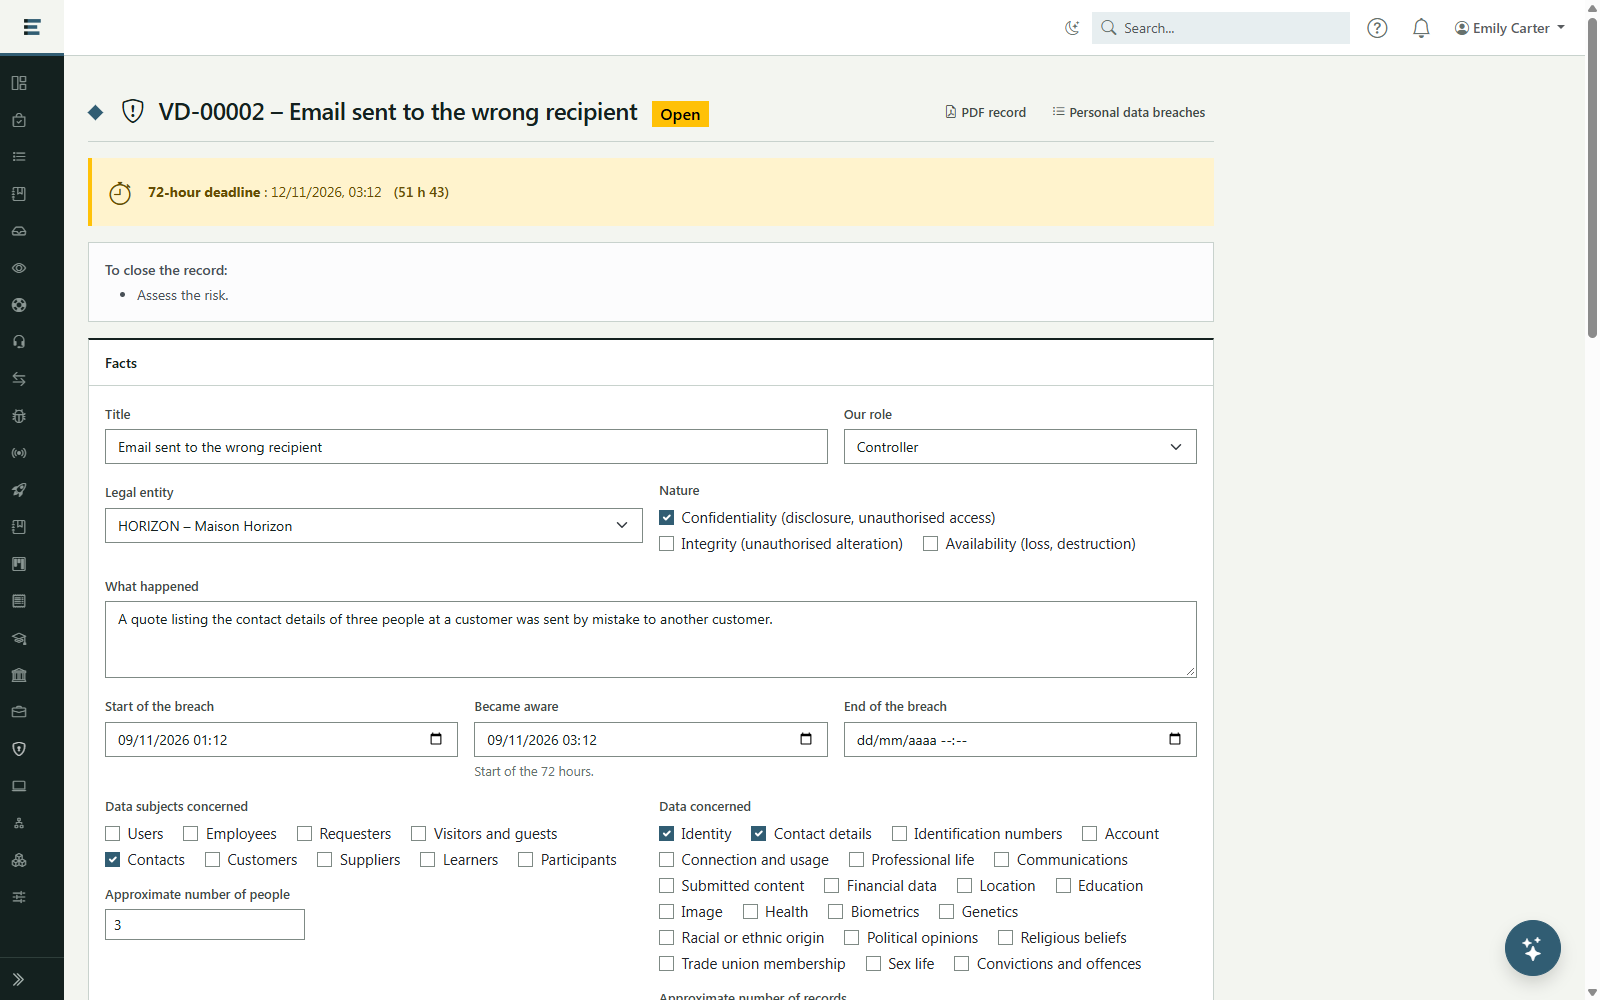
Ecaldima data protection: personal data breach record with its 72-hour deadline, the time remaining and what is still needed to close it.

01A data breach

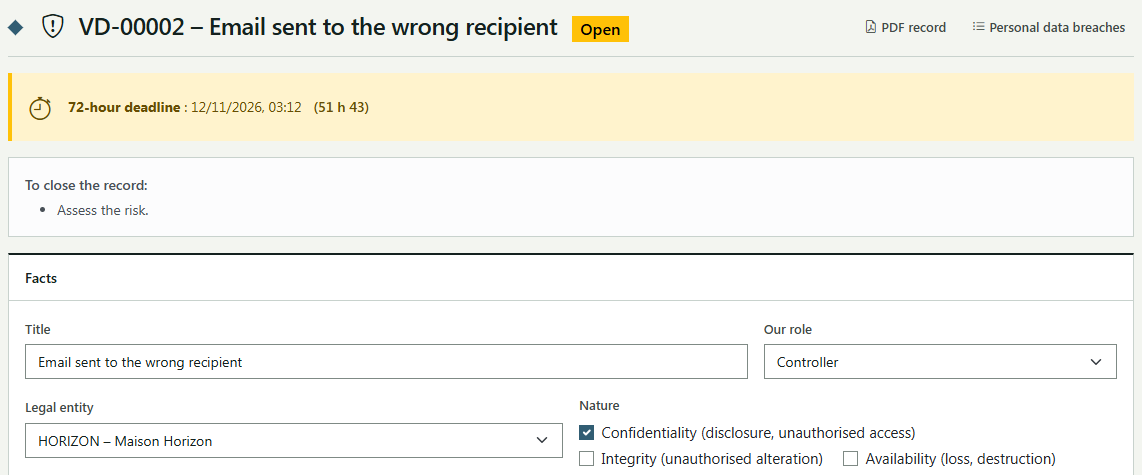
The 72-hour countdown calculates itself.

As soon as you become aware of a breach, the record shows the notification deadline and the time remaining, with alerts at 24 hours and at 6 hours. It cannot be closed while an obligation is outstanding: risk assessment, notification, informing individuals.
The 72-hour countdown calculates itself.

02A data subject request

An access or erasure request, carried out across the whole application.

Identity checked, a preview of the data found in each module, then a traceable execution. Whatever the law requires you to keep is refused with its reason, and external systems receive a task with its deadline.

03The data protection officer

Everything that needs action, on a single screen.

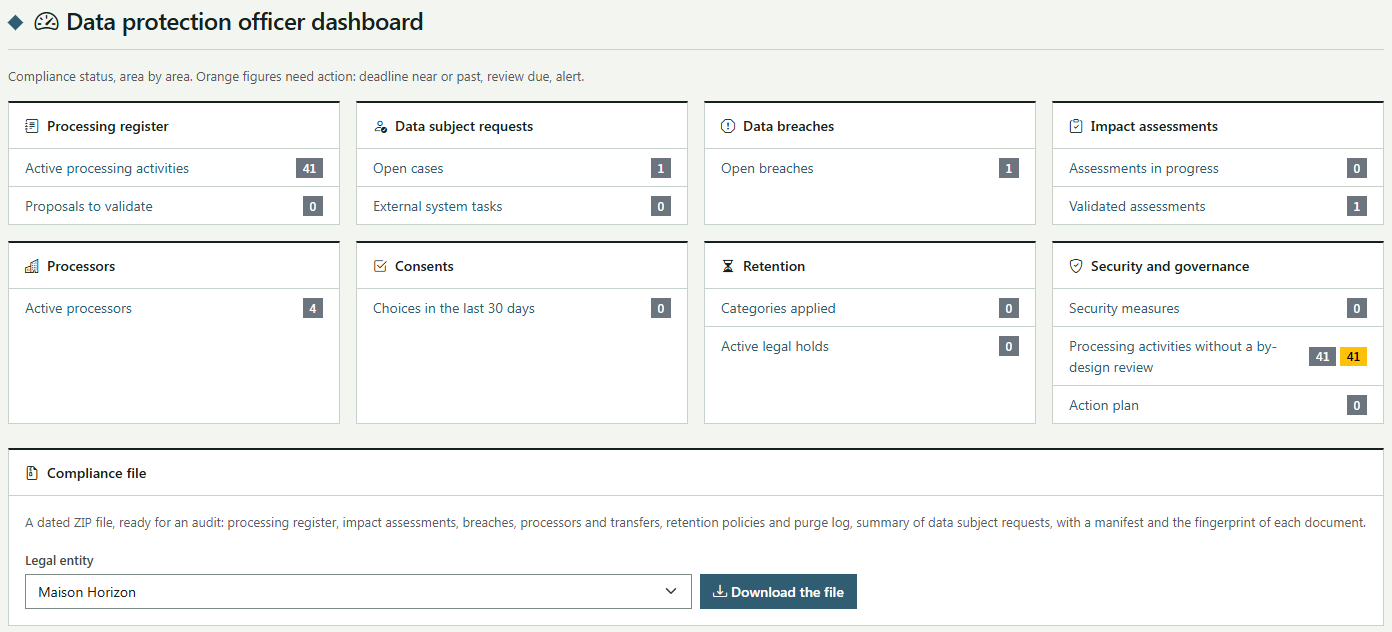
Requests coming due, open breaches, impact assessments, reviews due: the data protection officer’s dashboard shows only figures, never identities. One click produces the entity’s dated file, with the fingerprint of every document.

Everything that needs action, on a single screen.

The record starts from what already exists.

The application’s modules propose their own processing activities; the data protection officer completes, approves or sets them aside. Processing carried out outside the application, such as payroll, has its place too.

The data protection officer stays in control.

Ecaldima equips your GDPR obligations without deciding for anyone: legal bases, opinions, approvals and notifications remain human, and every decision is dated. Country templates are a starting point, to be reviewed by your lawyer.

I’m blown away!

A customer who has used Ecaldima since its early days, after the demonstration of the new version

Related modules

Functional scope Every detail of the module
  • Record of processingTwo records per legal entity, as controller (Art. 30.1) and as processor (Art. 30.2); checks on saving (purpose, sensitive data, transfers); dated versions, periodic review with reminder; PDF and CSV export, CSV import.
  • Data subject requestsAccess, portability, rectification, erasure, restriction and objection (Art. 15 to 22); identity check, preview without changes, confirmation by the data protection officer before execution; whatever the law requires you to keep is refused with its reason; access package in JSON with a readable PDF report.
  • External systems and recipientsOne task per processing activity held outside the application, with deadline, reminder and evidence; recipients informed after a rectification, erasure or restriction (Art. 19).
  • Retention periodsPeriods taken from the record; simulation by default, then application decided category by category (anonymise or delete); justified legal hold; intermediate archive with restricted access; purge log.
  • Processors and transfersArt. 28 agreement and its clauses, legal basis for transfers outside the Union, alerts on expired agreements; when you are a processor: published list of sub-processors, generated data processing agreement, acceptance by your customers with evidence.
  • Impact assessmentsQuestionnaire on the EDPB criteria, risks rated before and after measures, action plan, opinion of the data protection officer and approval; consultation of the authority tracked when the residual risk remains high.
  • Consent and information“My consents” area with history and one-click withdrawal, withdrawal link in emails; information notices (Art. 13-14) built from the record in collection forms, with the version read kept; Cookies and trackers page.
  • Data breachesRegister of all breaches, 72-hour deadline with alerts, notification to the authority and communication to individuals (Art. 33-34); closure impossible while an obligation is outstanding.
  • Security measuresRegister of measures per entity; the application flags those it observes itself (encryption, chained logs, two-factor authentication); data protection by design and by default review per processing activity.
  • Data protection officer’s areaDashboard with figures only, no identities; tasks, action plan and annual report; dated file per entity, with fingerprints and a list of missing documents.
  • Country templatesRules that depend on the country (deadlines, age of consent, authority) come from an importable template; templates for the European Union, France, Spain and Colombia are a starting point, to be reviewed by your lawyer.
  • ReversibilityAt the end of the contract, an archive of the instance’s personal data and files, in JSON Lines with fingerprints; download logged.

Integrations

  • Regulated requests and complaints: desk for data subject requests
  • Service Desk and major incidents: opening a breach
  • CRM: objections and consent respected before any message is sent
  • Contracts and Purchasing: processor records
  • Document templates: customisable PDFs and emails
  • API for the record and the file per entity

Prerequisites

  • One legal entity per company, with its country
  • A group of data protection officers and, if needed, of processing owners
  • Retention periods entered in the record before any purge
  • The Regulated requests and complaints module, optional, to receive requests

Want to see this module on your own processes?

We will build the demonstration around your operational reality.

Request a demonstration